


A critical bug in Apache’s HTTP/2 module can let an unauthenticated attacker run code on a web server. If your website runs on Apache, here is how to check whether you are exposed and what to do today.
Key takeaways
- CVE-2026-119618 is a critical flaw in mod_http2, the HTTP/2 module of Apache HTTP Server, that can lead to remote code execution (RCE).
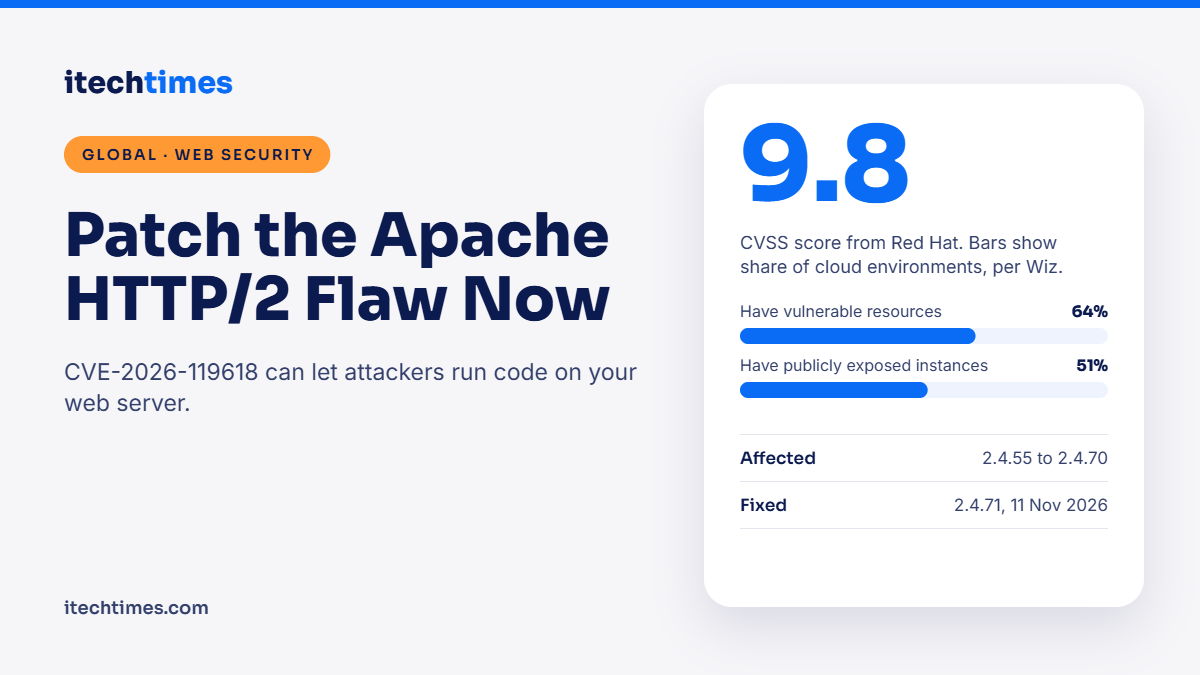
- Affected versions are Apache HTTP Server 2.4.55 to 2.4.70, plus standalone mod_h2 releases 2.0.8 to 2.0.42. The fix is in Apache 2.4.71, released on 11 November 2026.
- Red Hat scores it 9.8 on the CVSS scale. Only servers with HTTP/2 (h2 or h2c) enabled are affected.
- Wiz says no public exploit or in-the-wild attacks had been reported when it published, while Red Hat says public research has shown a reliable exploit against default configurations with mod_http2 enabled.
- If you cannot patch right away, disable HTTP/2 by setting Protocols to http/1.1, as Wiz recommends.
What is CVE-2026-119618 and should you worry? It is a critical remote code execution bug in Apache HTTP Server’s HTTP/2 module. Any site running Apache 2.4.55 to 2.4.70 with HTTP/2 switched on is at risk. Update to Apache 2.4.71 as soon as your hosting provider or Linux distribution makes it available, or turn off HTTP/2 until you can.
What is the Apache HTTP/2 vulnerability?
Apache’s official security page describes CVE-2026-119618 as a race condition, technically “concurrent execution using shared resource with improper synchronization”, in the assign_headers() function of mod_http2. Exploiting it can corrupt heap memory and lead to remote code execution.
In plain terms, an attacker who can reach your web server over HTTP/2 could send crafted traffic that lets them run their own code on the server, without needing a username or password. That could mean a defaced website, stolen customer data or a server quietly turned into part of a botnet.
The Apache project rates the issue critical. Red Hat gives it a CVSS score of 9.8, though it rates the impact on its own RHEL 9 and 10 builds as Important because of how those builds allocate memory for each HTTP/2 stream.
Which Apache versions are affected?
| Software | Affected versions | Fixed in |
|---|---|---|
| Apache HTTP Server (mod_http2) | 2.4.55 to 2.4.70 | 2.4.71 |
| Standalone mod_h2 (GitHub) | 2.0.8 to 2.0.42 | No new release listed by The Hacker News; the repository was archived on 9 June |
| RHEL 9 | Affected | mod_http2-2.0.26-7.el9_9.1 |
| RHEL 10 | Affected | mod_http2-2.0.29-5.el10_3.1 |
| RHEL 6, 7 and 8 | Not affected | Not needed |
Distribution status at the time of The Hacker News report: Debian unstable had the fix in apache2 2.4.71-1, while Debian bookworm, trixie and forky were listed as vulnerable with no fix yet. Amazon Linux 2, 2023 and 2027 Preview showed fixes as pending. Check your distribution’s security tracker for the latest status.
Note that sites which upgraded to 2.4.67 in May to fix an earlier HTTP/2 bug, CVE-2026-23918, are still affected by this new flaw until they move to 2.4.71.
What else does Apache 2.4.71 fix?
The same release patches two more issues, so it is worth installing even if you do not use HTTP/2.
| CVE | Module | Severity | Affected versions |
|---|---|---|---|
| CVE-2026-119618 | mod_http2, heap corruption and RCE | Critical | 2.4.55 to 2.4.70 |
| CVE-2026-106023 | mod_md, NULL pointer dereference crash | Important | 2.4.30 to 2.4.70 |
| CVE-2026-109163 | mod_vhost_alias, 1 byte stack overwrite | Low | 2.4.69 and 2.4.70 |
How was the flaw discovered?
According to Apache’s advisory, the bug was reported to the Apache security team on 26 October 2026 by Anthropic’s OSS Scanner, and separately on 3 November 2026 by Anthony Weems and Simon Scannell of Google Cloud Vulnerability Research. The fix was committed and version 2.4.71 was released on 11 November 2026.
How big is the exposure?
Cloud security firm Wiz says 64% of cloud environments it monitors have resources vulnerable to the flaw, and 51% have publicly exposed instances. Wiz notes these numbers do not account for configuration, so a server that has HTTP/2 disabled would not actually be exploitable.
| Wiz exposure data | Share of cloud environments |
|---|---|
| Have vulnerable resources | 64% |
| Have publicly exposed instances | 51% |
What does it mean for Indian websites and developers?
Apache remains a common choice on shared hosting, cPanel-style servers and self-managed VPS setups that many Indian small businesses, colleges, news sites and startups rely on. Sites on these setups that have switched on HTTP/2 for speed are exactly the ones that need attention here.
If you run a site in India, the practical risk is not just downtime. A compromised server can expose customer details, payment page scripts or login data, which can trigger incident reporting duties to CERT-In and a loss of customer trust. If you use managed hosting, the patch is your provider’s job, but you should confirm it has been applied.
What should you do today?
- Find your Apache version. Run
apachectl -vorhttpd -von the server. Anything from 2.4.55 to 2.4.70 needs action. - Check whether HTTP/2 is on. Search your Apache configuration, including every virtual host file, for a
Protocolsline containingh2orh2c. The directive can be set server-wide or per virtual host, so check both. - Patch. Install Apache 2.4.71 or your distribution’s fixed package as soon as it is available, then restart Apache.
- If you cannot patch yet, turn off HTTP/2. Change the directive to
Protocols http/1.1, removingh2andh2c, and restart. Apache’s advisory offers no other workaround. - Ask your host. If you are on shared or managed hosting, raise a ticket asking whether the server is patched or HTTP/2 is disabled.
- Watch your logs. Look for unusual crashes of Apache child processes, new unknown files in web directories or unexpected outbound connections.
Frequently asked questions
Is my WordPress site affected?
WordPress itself is not the issue. Your site is at risk only if the web server underneath it is Apache 2.4.55 to 2.4.70 with HTTP/2 enabled. Sites on Nginx or LiteSpeed are not affected by this specific bug.
Is this flaw being exploited right now?
When Wiz published its analysis, it said no exploit was available and no exploitation in the wild had been reported. Red Hat, however, says public research has demonstrated a reliable exploit, so you should treat patching as urgent.
Will turning off HTTP/2 slow down my website?
Your site will fall back to HTTP/1.1, which can be a little slower for pages with many files. It is a temporary trade-off that removes the risk until you can patch.
Does a CDN protect me?
It depends on how the CDN connects to your origin server. If your Apache server accepts HTTP/2 connections directly from the internet or from the CDN, it can still be exposed. Patching the origin is the safe option.
Which Linux distributions have fixed it?
At the time of reporting, Red Hat had fixed packages for RHEL 9 and 10, and Debian unstable had apache2 2.4.71-1. Debian stable releases and Amazon Linux were still awaiting fixes, so check their security trackers.
What is mod_http2?
It is the Apache module that adds support for the HTTP/2 protocol, which lets browsers load many files over a single connection. It is enabled through the Protocols directive.
Sources
- Apache HTTP Server 2.4 security vulnerabilities (official advisory)
- The Hacker News: Critical Apache HTTP/2 Flaw Could Let Unauthenticated Attackers Execute Code Remotely
- Wiz: CVE-2026-119618 RCE in Apache HTTP Server
2 thoughts on “Apache HTTP/2 Flaw CVE-2026-119618: Patch to 2.4.71 Now”